Thursday, 15 June 2017

OpenCV installation for Ubuntu

OpenCV installation for Ubuntu 

To install OpenCV 2.4.2 or 2.4.3 on the Ubuntu 12.04 operating system, first install a developer environment to build OpenCV.
    sudo apt-get -y install build-essential cmake pkg-config
Install Image I/O libraries
    sudo apt-get -y install libjpeg62-dev 
    sudo apt-get -y install libtiff4-dev libjasper-dev
Install the GTK dev library
    sudo apt-get -y install  libgtk2.0-dev
Install Video I/O libraries
    sudo apt-get -y install libavcodec-dev libavformat-dev libswscale-dev libv4l-dev
Optional - install support for Firewire video cameras
 sudo apt-get -y install libdc1394-22-dev
Optional - install video streaming libraries
 sudo apt-get -y install libxine-dev libgstreamer0.10-dev libgstreamer-plugins-base0.10-dev 
Optional - install the Python development environment and the Python Numerical library
    sudo apt-get -y install python-dev python-numpy
 
Optional - install the parallel code processing library (the Intel tbb library)
    sudo apt-get -y install libtbb-dev
Optional - install the Qt dev library
    sudo apt-get -y install libqt4-dev
Now download OpenCV 2.4 to wherever you want to compile the source.
    mkdir xxx
    cd xxx 
    wget http://sourceforge.net/projects/opencvlibrary/files/opencv-unix/2.4.2/Op...
or  
   wget http://sourceforge.net/projects/opencvlibrary/files/opencv-unix/2.4.3/Op...
file given above are old releases please follow this link to get the latest version of the opencv http://opencv.org/releases.html    

tar -xvf OpenCV-2.4.*.tar.bz2
Create and build directory and onfigure OpenCV with cmake. Don't forget the .. part at the end of cmake cmd !!
    cd OpenCV-2.4.*
    mkdir build
    cd build
    cmake -D CMAKE_BUILD_TYPE=RELEASE -D CMAKE_INSTALL_PREFIX=/usr/local
    -D WITH_TBB=ON -D BUILD_NEW_PYTHON_SUPPORT=ON -D WITH_V4L=ON 
    -D INSTALL_C_EXAMPLES=ON -D INSTALL_PYTHON_EXAMPLES=ON 
    -D BUILD_EXAMPLES=ON -D WITH_QT=ON -D WITH_OPENGL=ON ..
Now compile it
    make
And finally install OpenCV
    sudo make install

Saturday, 10 June 2017

Flashing/Installing stock MIUI image to the Rooted Redmi Devices and Fixing the Error 7

If you been wondering why the latest images of Android 7.1 Nougat based Lineage OS or RM OS are not working during the flashing processes showing some kind of Error 7,
Well there are 2 Solution for this problem


1) Edit the Android image zip file yourself remove the line of code regarding to devicename in the
following file which is responsible for this Error 7.
Open the Lineage OS ROM zip using any archiving software like 7zip, WinRAR, etc… You can also open it on your device.
  • Now, you need to navigate to this path: META-INF » com » google » android » updater-script.
  • Open the file updater-script in a text editor. You’ll see a bunch of lines with the command assert and the model name of the device next to it.
  • If there’s a mismatch with the codename of the device in the script, you’ll get Error 7 while flashing.
  •   
  • So, just either edit the code to match your device’s codename or delete all the lines having the code “assert & getprop”
  • Save the file.
  • Try to install the ROM now.


2) Install the Stock image of the Device in this case its the MIUI 8 from the Redmi

here is the link for it http://en.miui.com/download-301.html
on the section of -

and you also need these two things

b) Download the SuperSu zip file from here to root your phone again. Save the zip file on your phone.
Link here http://www.supersu.com/download

c) Download the lazy flasher zip file here to fix the boot loop issue. Yes, you nee to flash this file to fix the boot problem. Save the zip file on your phone internal memory.

Stable ROM

Click on Download Full Stock ROM if you have not yet rooted the device then you can follow there official guide for it that has been linked next to the download button there.
Else follow this blog.

 
 1. Download all the three files mention above and save all the file on your phone and remember the location of the files.

 2. Now open the updater application on your phone and Tap on the tap on three dots from top right corner and select “Reboot to Recovery Mode.”

 3. Now your phone will boot in the custom TWRP recovery mode.

 4. From here tap on the Wipe > Advanced Wipe and Select Dalvik Cache and Cache > Swipe to Wipe.

 5. After that go back to the main menu of the TWRP recovery. Select Install and Locate the MIUI 8 Recovery Full ROM zip file and flash the same on your phone.

 6. After flashing the ROM, Flash the Super Su zip file to get the Root access, and after that Lazy flasher zip file to fix the boot issue.

 7. Now reboot the system.


1. Download all the three files mention above and save all the file on your phone and remember the location of the files. 2. Now open the updater application on your phone and Tap on the tap on three dots from top right corner and select “Reboot to Recovery Mode.” 3. Now your phone will boot in the custom TWRP recovery mode. 4. From here tap on the Wipe > Advanced Wipe and Select Dalvik Cache and Cache > Swipe to Wipe. 5. After that go back to the main menu of the TWRP recovery. Select Install and Locate the MIUI 8 Recovery Full ROM zip file and flash the same on your phone. 6. After flashing the ROM, Flash the Super Su zip file to get the Root access, and after that Lazy flasher zip file to fix the boot issue. 7. Now reboot the system.


b) Download the SuperSu zip file from here to root your phone again. Save the zip file on your phone. c) Download the lazy flasher zip file here to fix the boot loop issue. Yes, you nee to flash this file to fix the boot problem. Save the zip file on your phone internal memory.


Monday, 5 June 2017

Highlights of WWDC 2017

I attended the World Wide Developer Conference of Apple and if you missed it or too busy to watch the lengthy keynote don't worry here it is-
In Total there are 8 new thing that came up in WWDC 2017

1 New Apple Watch OS 4.
2 Upgrades to Macbook.
3 New iMacPro.
4 Mac OS 11 High Sierra.
5 New iPad Pro.
6 HomePod.
7 ARKit
8 iOS 11


1 New Apple Watch OS 4


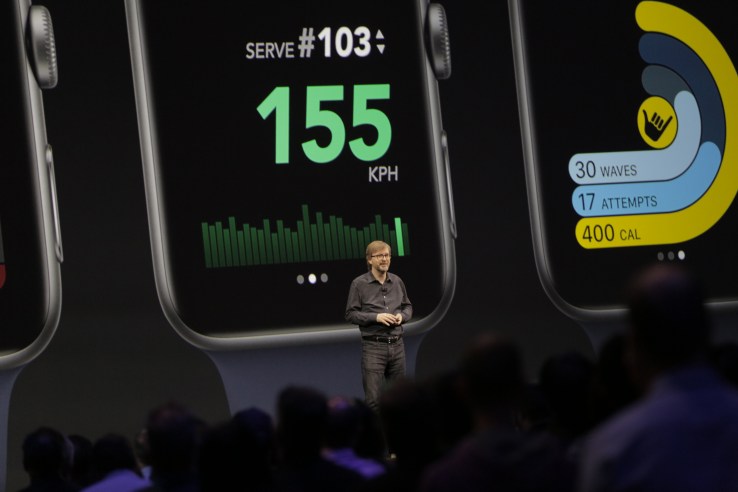
The Apple Watch has developed a new watch OS: Watch OS 4. Here are some of the important bits:

  1. There are new faces including a kaleidoscope and some Toy Story animations
  2. An increased focus on fitness allows for better tracking during runs and swims. There's also more encouragement for setting and achieving goals.
  3. The Apple Watch will automatically sync with fitness equipment from some of the biggest manufacturers to track your suffering.
  4. A new Music app has a redesigned interface.
  5. Native Bluetooth support allows the watch to communicate with small devices like a glucose monitor for diabetics.
  6. H.265 video supports HDR footage with 40% better compression to save space.


2 Mac and iMac


New MacBook Pros

All the MacBook and MacBook Pro are getting new Kabylake Processors from Intel (including MacBook Air).
Other big changes came in iMac
The venerable iMac computer is getting a refresh across a variety of specs. The screen is getting brighter, the max memory specs are doubling, and they're getting a pair of USB-C ports on the back for connecting fast storage.
  1. The 21.5-inch lower level model is getting a serious uptick in terms of graphic processing, which makes it 80% faster than before. 
  2. The 21.5-inch iMac 4K Retina now moves to discrete graphics, which makes it three times faster than the previous generation.
  3. The 27-inch 5K iMac goes up to 8 GB of VRAM, which can push up to 5.5-teraflops of computing power so it can handle VR development.
  4. Kaby Lake processors are coming across the board.

3 iMacPro

iMac Pro
The typical iMac can't handle super hardcore workstation stuff like machine learning development or real-time 3D rendering, so Apple build the iMac Pro. 
  1. Up to 18 cores of Xeon processing power
  2. AMD Radeon Vega graphics will handle the GPU roll.
  3. Up to 22 teraflops of computing power at the high-end which is a crazy amount. 
  4. It can have up to 128 GB of ECC memory
  5. Storage goes up to 4 terabytes built in. 
  6. It has 4 Thunderbolt ports and built-in 10 gigabit ethernet.
  7. Priced at $4,999 in December.

4 macOS High Sierra

The new version of macOS comes with a slight name change and a grip of new features.
  1. Apple now claims Safari is the fastest browser. 
  2. Auto play blocking in Safari detects videos with sound and blocks them, which is excellent.
  3. Safari's Intelligent Tracking prevention uses machine learning to identify cross-site tracking services. By, umbrella ads I see on every website.
  4. Photos gets improved search and better facial recognition. Tagging system is also synced across all devices if you're a neat freak about your images.
  5. Photos now gives you access to curves, which makes me very happy as a photography nerd. It's for advanced editing.
  6. Apple is opening its photo book printing service up to third party printers, which makes Microsoft's recent announcement about photo book printing seem weak.
  7. Public beta coming this month, free update coming in Fall as usual.
  8. Apple is releasing a new file system called APFS which is going to more performance cruncher.

5 iPad Pro 10.5-inch


iPad Pro
So a new iPad Pro today and it has a bigger screen with a smaller bazel.

  • 20% larger than the 9.7-inch, with a smaller border. 
  • It still weighs just a pound.
  • A10X Fusion with a six-core CPU and 12-core GPU which makes it 30-40% faster than the previous version across the board.
  • It's big enough to give a full-sized on-screen keyboard.
  • 120 Hz refresh rate makes scrolling and responses faster.
  • Apple Pencil now has just a 20 millisecond latency so it's more like writing. It's also 1 millisecond faster than Microsoft's Surface Pen.
  • Screens across the range will get 50% brighter.The screens also now have the color gamut for HDR video.

6 HomePod

Apple Home PodThis is the very exciting smart speaker launched by apple today. Here are the details on Apple's new smart home speaker.
  1. Siri is baked in and listens to you via six built-in microphones. It's built with the idea that you'll have an Apple Music subscription, of course.
  2. There's a HomeKit base built in, so you can use it to control smart home devices. Apple isn't focusing on this aspect as much as it is the sound quality, though.
  3. Spatial awareness helps it recognize the space it's in to tune the sound accordingly.
  4. Powered by an A8 chip that also powers the iPhone.
  5. There's a 4-inch woofer and the speaker itself is around 7-inches tall.
  6. It starts shipping in December for $349.

7 ARKit

With ARKit Apple is diving deep into the world of augmented reality, which is something that Microsoft and Google have been big on lately. It can place virtual objects on real-life surfaces in the world.
Apple ARKit
ARKit is going to let developers produce more augmented reality stuff. There's an AR Lego demo which sounds great because I can play with Legos, but not step on them.
Apple has taken this new step in Augmented Reality trend,

8 iOS 11

Apple started off its iOS 11 presentation by taking a shot at Google's Android fragmentation problem. No punches pulled there.
  1. Messages gets an update for to help sync messages across devices more efficiently as you sign in. 
  2. Apple Pay now operates on a person-to-person level so you can settle up with your friends after going out to eat.
  3. Siri is getting more conversational voices! 
  4. Siri will also now be able to do real-time translation so it can act as a go-between for people who don't have a common language.

Camera and Photos

  1. HEVC is the new format for video, which gives increased fidelity with smaller files.
  2. HEIF gives better quality photos at 2x compression.
  3. Portrait Mode in the camera now gets HDR and optical image stabilization.
  4. Machine learning recognizes different events and automatically creates slideshow-style presentations.
  5. They have embedded ML(Machine Learning ) inside the new iOS 11 to use the Apple Pencil more perfectly and to render graphics for the photos app like selecting a curve area etc.
That is all that happened today, Although more eyes will be on the September 2017 event of apple when it will launch the new IPhone8 which is going to be the most promising flagship smartphone.

Wednesday, 31 May 2017

Why using pirated windows is still a bad Idea

Using pirated windows is very bad idea from a security point of view -as these pirated copies of the windows are not secure enough as they will not get patched for critical security updates from Microsoft even if force try to update them then Microsoft server will catch your system based on fake licenses number and will block you from windows updates and disable several features including server capabilities and desktop wallpaper and software updates from windows update server.
Now you might be interested to know what kind of security risk are we talking about here so let get into it.

So I analysed a pirated copy of windows using a anti malware software and at the very first scan it found 4 infections of several kind of malware and key loggers.
now you want to know what malware it "malware is harmful piece of software that can cause damage to you data and exploit you system for any personal information "

Keylogger are the special program made to monitor each key stroke on the keyboard that you make these are used to steal your banking details credit card number and debit cards online banking passwords and system passwords for files and application like Password manager the dirty hacker who planted these harmful software in the pirated copy of windows can steal your identity and cause some serious damage to your virtual, reputation and real life they can empty your bank account in seconds and make you homeless.


this scan shows the infection type found in the core windows system files.


This is example what the infected pirated windows did its malware activated as soon as you powered the system and it downloaded a fake copy of visual basic name file which is actually a key logger that will monitor and send each key you press on your keyboard to the hacker through which they know everything you are typing those malware also has capabilities to install a RAT in your system.

A RAT is Remote Administrative Tool through which they can literally they can control your computer without physically touching it and can make your life more miserable.


here is what a security expert said about this issue-

Windows, after having dropped it's embedded ad's (see: One Drive Ad, now a part of explorer) - the feature could be further exploited to plant 'malware', 'spyware' & have the explorer infected from unknown sources.
That's a big hit & a broad risk. Shouldn't be any if you go all into Linux Core, as you're in control from the very scratch. If rich, go Mac - that's pretty decent as well. - Shritam Bhowmick Application Security Expert.


I don't want to promote Microsoft windows and there product here this is not a sponsored article but its better to use either original windows or if you can't buy it then don't use windows at all use Linux distributions like Ubuntu Debian or Mint which are great for starters in Linux community.

If you can afford to spend some more money I will suggest buying a Mac which is a perfect combination of security of unix plus performance of apple brand.

Again I am here if you have any question related to any topic in this field.

Please share and comment.


Wednesday, 26 April 2017

Backdoor In WhatsApp really?


Introduction

A security vulnerability that can be used to allow Facebook and others to intercept and read encrypted messages has been found within its WhatsApp messaging service.

Facebook claims that no one can intercept WhatsApp messages, not even the company and its staff, ensuring privacy for its billion-plus users. But new research shows that the company could in fact read messages due to the way WhatsApp has implemented its end-to-end encryption protocol.

Establishing the Case
Should I be worried about the WhatsApp encryption backdoor?
Privacy campaigners said the vulnerability is a “huge threat to freedom of speech” and warned it could be used by government agencies as a backdoor to snoop on users who believe their messages to be secure.

Recognize the Issue

WhatsApp has made privacy and security a primary selling point, and has become a go to communications tool of activists, dissidents and diplomats.

WhatsApp’s end-to-end encryption relies on the generation of unique security keys, using the acclaimed Signal protocol, developed by Open Whisper Systems, that are traded and verified between users to guarantee communications are secure and cannot be intercepted by a middleman.

However, WhatsApp has the ability to force the generation of new encryption keys for offline users, unbeknown to the sender and recipient of the messages, and to make the sender re-encrypt messages with new keys and send them again for any messages that have not been marked as delivered.

The recipient is not made aware of this change in encryption, while the sender is only notified if they have opted-in to encryption warnings in settings, and only after the messages have been re-sent. This re-encryption and rebroadcasting effectively allows WhatsApp to intercept and read users’ messages.

Addressing the Issue

The security loophole was discovered by Tobias Boelter, a cryptography and security researcher at the University of California, Berkeley. He told the Guardian: “If WhatsApp is asked by a government agency to disclose its messaging records, it can effectively grant access due to the change in keys.”

The vulnerability is not inherent to the Signal protocol. Open Whisper Systems’ messaging app, Signal, the app used and recommended by whistleblower Edward Snowden, does not suffer from the same vulnerability. If a recipient changes the security key while offline, for instance, a sent message will fail to be delivered and the sender will be notified of the change in security keys without automatically resending the message.

WhatsApp’s implementation automatically resends an undelivered message with a new key without warning the user in advance or giving them the ability to prevent it.

Boelter reported the vulnerability to Facebook in April 2016, but was told that Facebook was aware of the issue, that it was “expected behaviour” and wasn’t being actively worked on. The Guardian has verified the loophole still exists.

But Officals at whatsapp has denied of any loop hole in the whatsapp platform and said “Over 1 billion people use WhatsApp today because it is simple, fast, reliable and secure. At WhatsApp, we’ve always believed that people’s conversations should be secure and private. Last year, we gave all our users a better level of security by making every message, photo, video, file and call end-to-end encrypted by default. As we introduce features like end-to-end encryption, we focus on keeping the product simple and take into consideration how it’s used every day around the world.

Stay tune for more inside news from Hackers Underground and information security.

Please suscribe to blog and press the share button if you like it,

see you later.

Tuesday, 21 March 2017

Cheat sheet for Reverse Engineering for Malware Analysis


Download the original size here link  http://www.datafile.com/d/TWpVM01UWTNNekEF9/cheat sheet reverse v6.png


Sharing is Caring :)

Sunday, 5 March 2017

Introduction to vtechcoder point of sale (pos) Software

Introduction to vtechcoder point of sale (pos) Software


Most advance POS Project can be used in more than 170 countries and supports 17 international language. works on Windows,Linux and Mac and other touch enabled POS Hardware for Business Outlets .


here is a rough list of features that i have already in place in pos
Aside from complete Billing system. 
• Touch and Click User Interface.
• Bar Code Scanning
• Cancellation
• Coupons
• Credit Card Processing
• Customer History
• Customizable GUI
• Discounts
• Layaways & Quotes
• Mobile POS Capability
• Multi-System Integration
• Multiple Payment Forms
• Offline Transactions
• Print Reciepts
• Receipt Notes
• Refunds/Returns
• Revenue Totals
• Store Credit
• Tax Exemption
• Time-Limited Specials
• Transaction Hold/Recall
• Report generation.


GST Tax system implementation included for all the GST tax supporting market around the globe. 

Cash Flow Report - Basic list of order totals.
Cash Flow Report Extended - List of order totals with some more
information including customer name, transaction number, tender used.
Category Sales - Sales by category
Closed Cash Report - Shows sum of tenders for each POS by closed cash
period. Small update - Added number of no sales per sequence.
Closed Cash Export - Closed Cash Report in simple excel exportable
format.
Chart Sales - Sales by category.... in chart form!
Closed Products - Shows all items sold during closed cash periods by
register.Customer Diary - will show you customer payment activity for a date
range that you select, and can be filtered by customer. (a value of rupees
will show all customers in that date range)
Customer Report - this will show you a listing of your customers with
information
Products - Listing of Products in list view by category
Product Catalog - Changed the name from Sales Catalog to be clearer
on what this report is. This will create a report showing all items in your
database with item name, category, sell price, total price (sell price + tax)
and the item image if there is one in the database in a tile type view.
Product Sold - List of all items sold ordered by date/time.
Reservations Report - Will list reservations per day
Sales by Customer - Sales by Customer (Will only show sales that do not
have null for customer column)
Sales Taxes - List all sales tax.
Top 10 Sales - List top 10 sales with a handy chart (Gross amount not qty).


For free demo of the project and for Questions and Business Queries email us at vishwa@vtechcoder.com    -
vtechcoder@gmail.com


You can also buy source code for your organisation to modify it according to your needs or we will do that for you with small charge.

if you prefer business using third part here is the link for that 

Tuesday, 24 January 2017

Privacy is a Myth


People say we are not being monitored, well how about this example this product i was checking on my super secure android device, but some how facebook know and shows be add of this on my facebook feed on my workstation,


No i don't have any adware installed,


Reason is facebook app monitors all activities that you do on your devices including internet browser history so it make sense the facebook android app is installed on my phone too.


Generally people don't realise how these big corporates exploiting there privacy,
well sure people will say its convenient to see those ads so you buy stuff that you were looking for but if you look at it its a thought of lazy person, when you realise that privacy is myth,


This is not it websites collect lot more data about there users like

Users Location
IP addresses

Device information

Broweser details
and more

To get more details about users like there like and dislikes they go for your bookmarks and browser history also its a treat for those data hungry monster website when you install there browser plugin then they literally monitor your system until your browser is on.

On more dark side if you are in the target list of any state hired or independent hacker then things can go more worst all the browsers are exploitable if you visit deep web you can find them and buy them too they are called zero days.

Of you are running a older version of browser then things becomes as easy as cake walk for hackers,
they can exploit you system and gain admin access to your operating system in just few commands and then they can do more dangerous things like Ransomware and identity theft they can ruin your life.

Now we have some kid tech lover who consider them self expert and they will say we use adblocker those ad malware can't get to me
well here is a thing kids
there are so many tracking techniques that are not embedded in the websites to track users activity even if you block there ads.
they make there website a living tracking bot some of those techniques requires user permission that they achieve by technique called Clickjacking or Alerts of java scripts.

i will soon write article about how to prevent yourself from such threats but for now here is my goodnight advice
>Stay updated always update your system and application software

>Disable java script on your browsers and flash

>Don't click on random content.
>Only download software or app on devices from trust able resource like Appstore or Playstore.

>Don't use pirated Windows (Use Linux if you can't afford genuine version).

>Uninstall third party app like facebook use fb.com on browser.

i'm not bluffing about fb tracking you checkout this article in WSJ Link
Sharing is caring :)

Thursday, 1 September 2016

Facebook Reaction: a privacy attack for corporate benefit.


Recently Facebook launched many images to be added in there post so that user can express their feelings in different different moods and smile sad happy but no one understand the reason behind it
Welcomes to earning money both Facebook and Google goes in same Direction they both are different words of same reason to use uses data and they sell them in order to more revenue.


     Earlier Belgian police gave  a public warning about the use of Facebook reaction buttons instead of like button check here

what Facebook has done it is limiting the users response to a particular post to 6 reactions,
By limiting the responses to a post to six emotions: which the social networks calls “Like, Love, Haha, Wow, Sad and Angry”,

To use this reaction data for advertising Facebook developed some algorithms that are used to determine the liking and not liking of a user for particular post or product,

Facebook's algorithms are able to measure your reactions more effectively, this means Facebook can now surf personalized advertisements to its user for its benefit,
for example if you press "Like" or "woow" reaction on a pizza joint then its most likely you will see a offer on the product from that brand.

What this arrangement actually does is that it increase the effectiveness of use profile to the Facebook and its partner companies about how there users are behaving towards the content that is showing in there feeds and this helps them a lot than just showing million people about same ads.
because now when you see thing of his preferences in the feed he or she is most likely to show a reaction to it and plan to buy that service or offer in future time.

Corporate benefits more from this as now Facebook has more accurate data about there users then it can sell this data two its partners and show more accurate ads and post to its users.

so although this reaction function is killing privacy with one more dagger but what we can do,
people can't stop using this just because they gonna get more customized content in there feed,

And who knows Facebook may also planning to use the data collected from this reaction algorithms to develop its Artificial Intelligence Program and source point of human knowledge and behavior.
we all know CEO of Facebook is working on A.I. since many ears now.

i think users need to protest against this and ask Facebook to remove this from the functionality which is very impossible to happen in near future.

thanks for reading please subscribe and share.


Sunday, 21 February 2016

Updating and upgrading friends GNU/Linux system without internet

If you ever get stuck in a situation where you have to update / upgrade a system or server but you can not plug it directly to the network then here is easy solution for this problem.
just follow these steps:-
  1. First Insert live-cd/usb of GNU/Linux (in this case ubuntu 14.04) in your system . 
     (warning: Install synaptic package manager before doing all these steps in your target friends computer, otherwise later due to dependency error you won't be able to do it.)
  2. press ctrl+alt+delete for opening the terminal ,and run

    sudo apt-get update

    sudo apt-get install synaptic
  3. Open /var/cache/apt/archives and save the contents in safe directory (for example on Desktop, use sudo for it -sometime you need to be little wild superuser for even copying task :)
  4. Update your system(live cd/usb) using update manger
  5. Install some softwares if you wish :-),

    Ie ,if you want ubuntu-restricted-extras Install ubuntu-restricted-extras ,

    run sudo apt-get install ubuntu-restricted-extras in terminal
  6. Install aptoncdInstall aptoncd 


  7. Launch aptoncd and press create button, It will create an iso file
    from here either you can create iso file which you can transfer to friends computer via usb stick or you can burn them to a dvd / cd disk.
  8. Goto your friends home/office with Generated iso and directory made for step3
  9. Copy the directory and iso file to the desktop , Open the terminal and move to that directory

    cd /path/to/directory
  10. Run sudo dpkg -i *.deb ,It will install synaptic
     
  11. Open the synaptic and clickEdit->add cdrom It will display a dialog box , Don't click on it.
  12. Return to terminal and run

    sudo mkdir /media/cdrom

    sudo mount -o loop /path/to/iso /media/cdrom
  13. Now press ok button on the dialog generated from synaptic in step11 , 
  14. Press Mark all upgrades , Apply buttons ,respectively 

  15. Your friends GNU/Linux system is updated , Now sit back and relax for few minutes.


Monday, 11 January 2016

FBI crack Tor and catch 1,500 subscribers of child pornography website on the dark web

   FBI crack Tor and catch 1,500 subscribers of child pornography website on the dark web


Yeah you heard right fbi can hack the tor network, but how we don't know yet, it comes under the

the court order can be seen here link by which fbi conducted this raid.


The fbi hacking tool that can identify IP and MAC addresses of devices.

TOR Network
The Onion Router (Tor) is software that anonymises your internet trafficTor Network
At its peak, Playpen website had around 215,000 members. It had more than 117,000 posts and it received an average of 11,000 unique visitors a week. The FBI discovered many posts featuring extreme child abuse imagery, as well as providing advice on how potential child sex abusers could avoid detection online.
After seizing the computer server running Playpen from a web host in Lenoir, North Carolina, in February 2015, the FBI decided to run the child pornography web site from its own servers in Newington, Virginia, for an additional two weeks between 20 February and 4 March of that year.
When visitors accessed the website, the FBI deployed a network investigative technique (NIT) – a hacking tool – and used a single warrant to uncover 1,300 IP addresses, tracing these addresses back to actual individuals.
The FBI has used NITs before, but this is the first time that it has been reported that the NIT was able to get around the protections of Tor. When visitors accessed the website, although their traffic might have been encrypted, a Flash application was secretly installed on the user's computer that quietly sent important data about the user straight to the FBI so that it did not pass through the Tor network at all, according to Motherboard Vice.
The NIT was able to capture the actual IP address of the computer, the type of operating system the user's computer was using, the computer's architecture, the computer's MAC address, the computer's host name, the computer's active operating system username and was even able to issue a unique identifier to the user in order to distinguish all data collected from another user's IP address.
Even though the method has undoubtedly helped to bring down child pornographers, the American Civil Liberties Union is concerned that the FBI was able to hack into over 1,000 computers with just a single warrant, and believes that Congress and the public should play a role in evaluating whether law enforcement should be allowed to use NITs at all.
Over 1,500 cases have resulted from the investigation

Two men were indicted in New York in July 2015 on child pornography charges, the first of many who were arrested throughout 2015. Many of the arrested will see their cases heard throughout the first half of 2016, and the court documents showed that charges were filed against defendants in Connecticut, Massachusetts, Illinois, New York, New Jersey, Florida, Utah and Wisconsin.
"Fifteen-hundred or so of these cases are going to end up getting filed out of the same, underlying investigation," Colin Fieman, a federal public defender for the Western District of Washington who is handling several of the related cases, told Motherboard Vice.
"There will probably be an escalating stream of these [cases] in the next six months or so," he added. "There is going to be a lot in the pipeline."
I am not saying fbi should not stop any child pornography scam or site, but what my point is if they passes capability to de anonymize tor user then we loose the main concept of using tor at the first place, we use this tool for complete anonymity not just to reduce our internet speed by intentionally bouncing traffic to different tor circuit just to reduce internet speed.

Alert:-
to continue being anonymous online i advise you use tor over a trusted vpn

Let me know you comments upon it and please share it.


Proper way to install nvidia 390 fix error

Proper way to install nvidia 390 if you see any error in the process look below; command  sudo apt purge --autoremove '*nvidia*...